간담회와 발제
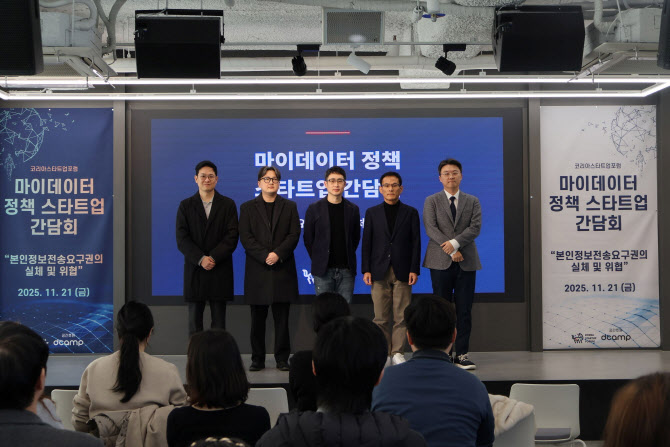
2025년 11월 21일, 코리아스타트업포럼의 「마이데이터 정책 스타트업 간담회」에서 본인전송요구권 확대와 스타트업에 미칠 영향에 관해 발제했습니다. 당시 현장 사진에는 행사명과 날짜가 표시되어 있습니다. 주최 기관의 활동 연혁에도 2025년 11월 간담회가 기록되어 있습니다.
발제에서 제기한 우려
제 관심은 정보주체의 권리를 확대하면서 기업이 투자해 구축한 데이터와 보안을 어떻게 함께 보호할 것인가에 있었습니다. 주문 패턴, 가격 전략, 고객 분석 자료 등을 모두 같은 성격의 데이터로 취급하기보다, 개인정보·가공정보·영업비밀의 경계를 따져야 한다고 보았습니다.
전송 방식의 보안성, 대리권의 범위, 관리 기관의 책임도 살펴볼 필요가 있다고 주장했습니다. 이는 당시 개정 논의에 대한 제 견해입니다. 특정 자료가 법적으로 영업비밀에 해당한다거나 제도가 위헌이라는 판정을 내린 것은 아닙니다.
정책 설계에 대한 의견
데이터 전송의 대상과 예외를 명확히 하고, 보안 사고와 부당한 이용에 대한 책임을 구체화하며, 기업 규모에 따른 이행 부담을 살펴야 한다고 생각합니다. 데이터를 활용할 기회와 데이터에 투자할 유인이 함께 유지되는 설계가 필요합니다.
이 글은 2025년 11월 발제의 관점을 정리한 기록입니다. 그 이후의 법령 개정이나 현재의 구체적 의무를 설명하는 글과는 구분합니다.
The discussion
On November 21, 2025, I spoke at the Korea Startup Forum’s MyData startup policy discussion about data-transfer rights and implications for startups. The event name and date appear in the photograph; the organizer’s history also records a MyData discussion in November 2025.
Concerns raised in my presentation
My focus was how to expand individuals’ rights while protecting security and data built through business investment. Order patterns, pricing strategies, and customer analysis should not automatically be treated as identical types of information; the boundaries between personal information, processed data, and trade secrets require examination.
I also argued for examining transfer security, the scope of delegated authority, and the responsibilities of data-management organizations. These were my views on the proposal at the time, not legal findings that particular information qualifies as a trade secret or that a measure is unconstitutional.
A policy-design perspective
Transfer requirements and exceptions should be clear, responsibility for security failures and misuse should be specified, and compliance burdens should be considered across business sizes. A workable design should sustain both opportunities to use data and incentives to invest in it.
This article records the perspective of the November 2025 presentation. It does not describe subsequent amendments or current case-specific obligations.